Skip to content

fix(ci): update codeql upload-sarif to v1.0.4 - #3727

Closed
jsjoeio wants to merge 1 commit into
mainfrom
jsjoeio-revert-codeql-action
Closed

jsjoeio wants to merge 1 commit into
mainfrom
jsjoeio-revert-codeql-action

Conversation

@jsjoeio

@jsjoeio jsjoeio commented Jul 6, 2021 •

Copy link
Copy Markdown
Contributor

This re-enables the trivy-scan-image job in ci which is used to scan our Docker image for vulnerabilities. We had to disable it due to this issue in codeql-action/upload-sarif: github/codeql-action#528

Fixes #3517

@jsjoeio jsjoeio self-assigned this Jul 6, 2021
@jsjoeio jsjoeio added chore Related to maintenance or clean up ci Issues related to ci security Security related labels Jul 6, 2021
@jsjoeio
jsjoeio marked this pull request as ready for review July 6, 2021 20:15
@jsjoeio
jsjoeio requested a review from a team as a code owner July 6, 2021 20:15
@codecov

codecov Bot commented Jul 6, 2021

Copy link
Copy Markdown

Codecov Report

Merging #3727 (21ef801) into main (102f811) will not change coverage.
The diff coverage is n/a.

Impacted file tree graph

@@           Coverage Diff           @@
##             main    #3727   +/-   ##
=======================================
  Coverage   61.55%   61.55%           
=======================================
  Files          35       35           
  Lines        1813     1813           
  Branches      365      365           
=======================================
  Hits         1116     1116           
  Misses        588      588           
  Partials      109      109           

Continue to review full report at Codecov.

Legend - Click here to learn more
Δ = absolute <relative> (impact), ø = not affected, ? = missing data
Powered by Codecov. Last update 102f811...21ef801. Read the comment docs.

@jsjoeio
jsjoeio marked this pull request as draft July 6, 2021 21:14
@jsjoeio

jsjoeio commented Jul 6, 2021

Copy link
Copy Markdown
Contributor Author

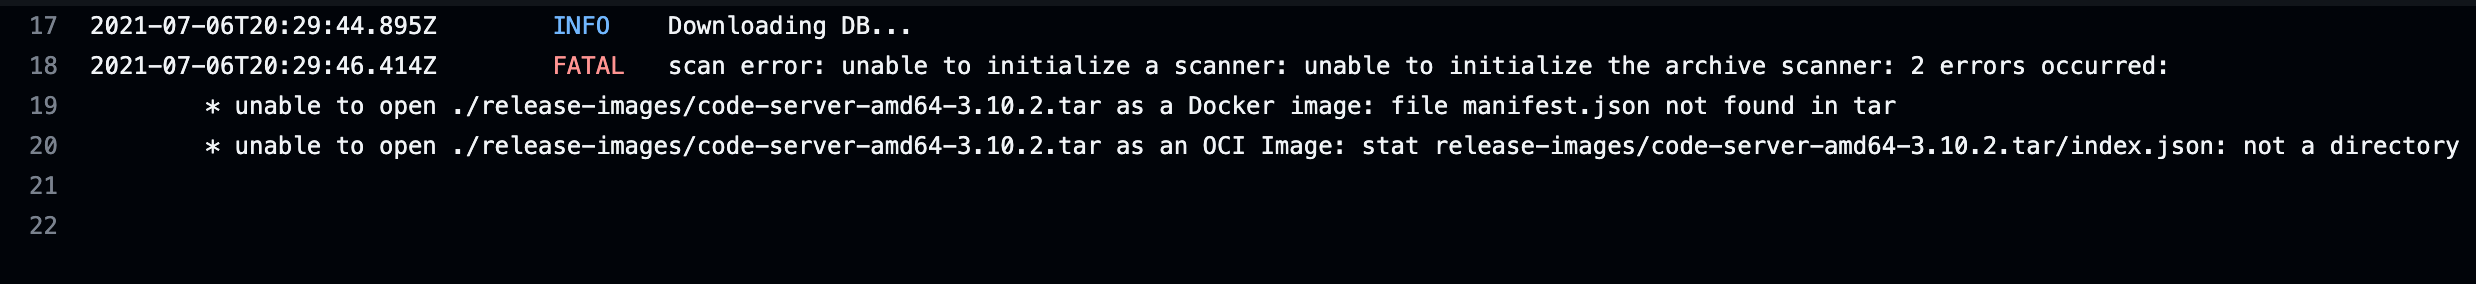
image

Weird, I swear it worked before but now I'm getting this error. Thinking out loud here...

  1. We build docker images and then upload them as artifacts under release-images
  2. In trivy-scan-image, we download those release images
  3. Then we run the Trivy vulnerability scanner and pass in the .tar file as input 🤔 Is this the correct thing to do? Looking under inputs in the docs, yes, .tar is expected.
  4. Looks like it wants a manifest.json in the Docker image, which we may or may not have...
  5. And it also wants index.json I think? hmm

@jsjoeio

jsjoeio commented Jul 6, 2021

Copy link
Copy Markdown
Contributor Author

@oxy any ideas?

@jawnsy

jawnsy commented Jul 6, 2021

Copy link
Copy Markdown

@jsjoeio You could also push the image to GitHub's container registry and then pull/scan from there, but we'd have to prune old images or else the cost will add up

@jsjoeio

jsjoeio commented Jul 6, 2021

Copy link
Copy Markdown
Contributor Author

Hmm...I've never used GitHub's container registry. (I would be worried that someone forgets to prune or something breaks with that flow and we get charged a lot 😂)

I'm open to it though! Would you recommend that instead?

@jsjoeio

jsjoeio commented Jul 7, 2021

Copy link
Copy Markdown
Contributor Author

Possibly related: aquasecurity/trivy#1080

@jsjoeio

jsjoeio commented Jul 7, 2021

Copy link
Copy Markdown
Contributor Author

GitHub's container registry

I looked into this and pushing is easy.

I found this action for deleting by tag

We could probably combine the three:

  1. Push to GitHub container registry
  2. Use with trivy-scan-image
  3. Delete from GitHub container registry

@jsjoeio

jsjoeio commented Jul 7, 2021

Copy link
Copy Markdown
Contributor Author

We also need to make sure the repo has access to the container packages.

@jsjoeio

jsjoeio commented Jul 7, 2021

Copy link
Copy Markdown
Contributor Author

After thinking about this a bit more, I've decided to put this on hold. It would take some time to set everything up for the GitHub Container Registry. I'd rather wait to see if we get a response on aquasecurity/trivy#1080 before taking on the work to make this happen.

@jsjoeio jsjoeio closed this Jul 7, 2021
@jsjoeio
jsjoeio deleted the jsjoeio-revert-codeql-action branch July 7, 2021 21:03
Sign up for free to join this conversation on GitHub. Already have an account? Sign in to comment

Labels

chore Related to maintenance or clean up ci Issues related to ci security Security related

Projects

None yet

Development

Successfully merging this pull request may close these issues.

Revert code-ql-action/upload-sarif

2 participants